Data protection · Contract law · Employment law
Your employee uses ChatGPT. Who sets the rules?
The risk may begin before the answer: when a document leaves your own environment.
Case status23 September 2026 edition · sources checked on 22 September.
01
The news: a national proposal, a local decision
On 16 September 2026, Vanessa Matz presented a proposed AI Strategy 2.0. The announcement describes a basis for developing a national strategy with Belgium’s federated entities, not a new general obligation on businesses. Its ambition to retain control of AI use nevertheless poses a practical question for SMEs and non-profits: who approves tools, for which documents and with which safeguards? [1]
On 29 May, Belgium’s Data Protection Authority highlighted risks in chatbot conversations. Free-text exchanges can include highly personal data; retention must be justified and uses explained. This was an Inspectorate communication, not a sanction decision concerning the fictional scenario above. [2]
02
A business account is not legal immunity
Where personal data are processed, the GDPR requires, among other things, a lawful basis, a defined purpose, data minimisation and appropriate protection. The controller must be able to demonstrate compliance. Purchasing a business licence does not, by itself, provide that demonstration. A product label cannot establish what actually happens to a particular document. [3]
Examine the organisation’s and provider’s actual roles. If the provider acts as a processor, Article 28 governs that relationship. A data protection impact assessment is required where the intended processing is likely to result in a high risk, not automatically whenever AI corrects a piece of text. [4]
Not all confidential information is personal data. Negotiated prices and business plans also require attention to contractual confidentiality commitments. Conversely, removing a name does not necessarily prevent identification through the remaining details. The assessment concerns the software, but also the content, context and destination of the information.
03
The Law Right approach: five rules before pasting
- Write a short rule identifying approved tools, permitted documents, excluded data, the person responsible for approval and the incident-reporting channel. Give employees a workable route when they are unsure.
- Check settings, access, retention and possible reuse by the provider. If personal data are transferred outside the European Economic Area, verify the applicable mechanism and necessary safeguards. This approach is not a Belgian compliance certificate. Verify your organisation’s actual configuration, not just marketing language. [5,6]
- Keep a person responsible for checking the output. Test the policy with a fictional document before applying it to real files. Record useful decisions without unnecessarily retaining confidential conversation content. A policy should make safer work possible, not merely relocate uncertainty to the employee.
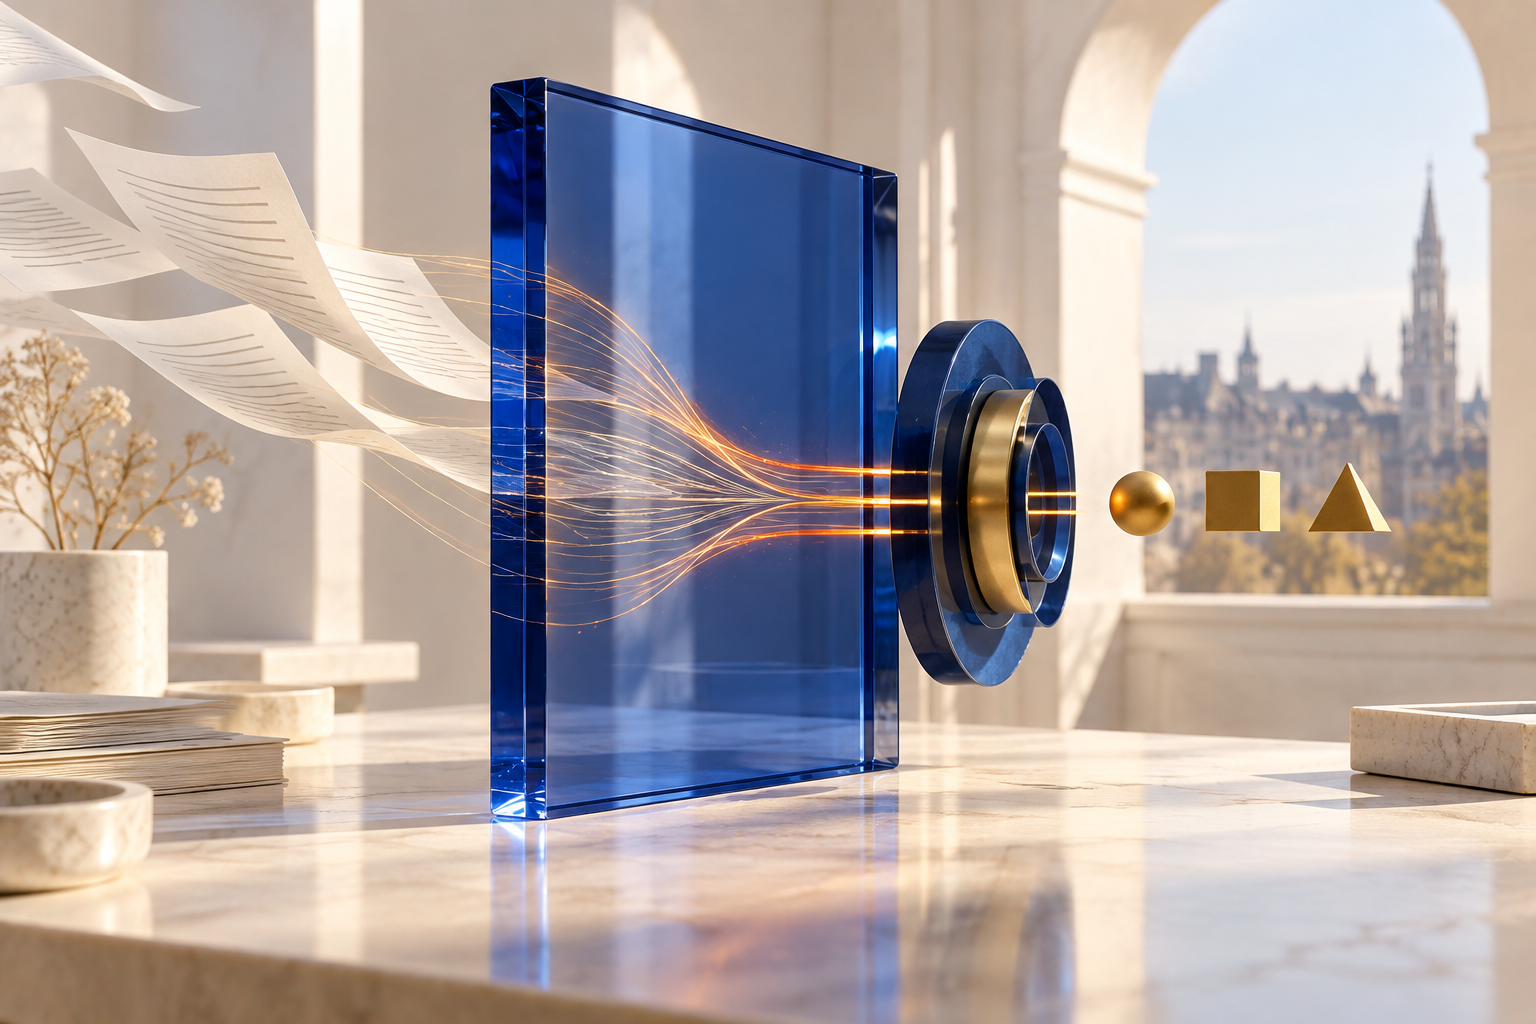
A boundary for your data.
Identify personal or confidential information before transferring it.
Conceptual illustration created with AI assistance — not real data or an automated legal outcome.A good AI policy does more than reassure in a folder. It helps people decide before they send.
Sources and verificationOpen the sources +
- primaryVanessa Matz · 16.09.2026 · Proposition de stratégie IA 2.0 ↗
- primaryAPD/GBA · 29.05.2026 · Chatbots et protection des données ↗
- primaryRGPD/GDPR · Articles 5–6 · Texte reproduit par la CNIL ↗
- primaryRGPD/GDPR · Articles 24, 28, 32–35 · Texte reproduit par la CNIL ↗
- primaryCNIL · 18.07.2024 · Déployer une IA générative ↗
- primaryRGPD/GDPR · Chapitre V · Transferts internationaux · Texte reproduit par la CNIL ↗